Apple Patches Critical Connectivity Flaws in Latest Software Rollout
Apple has released a suite of urgent updates across its ecosystem today, deploying iOS 27.2.1, iPadOS 27.2.1, and macOS 27.2.1 to address several concerning security gaps. While the company hasn’t confirmed whether these vulnerabilities have been exploited by hackers yet, the nature of the fixes suggests that users should install them immediately to avoid potential risks now that the technical details are public knowledge.
Much of the focus in this update centers on connectivity and messaging privacy. Engineers patched a particularly worrying iMessage flaw that could have allowed remote attackers to sneak into group chats or view message histories from before they ever joined the conversation. Even more alarming were discoveries regarding Bluetooth and AirPlay, including a bug where a malicious Bluetooth device could pair with a phone without any user consent and another that left process memory open to corruption by nearby attackers.
For those on Mac computers, the latest version includes additional safeguards for command line tools specifically designed to mitigate the eMudhra certificate vulnerability. Most of these issues were identified internally by Apple’s own security teams rather than external researchers, showing a proactive approach to hardening their systems against increasingly sophisticated threats.
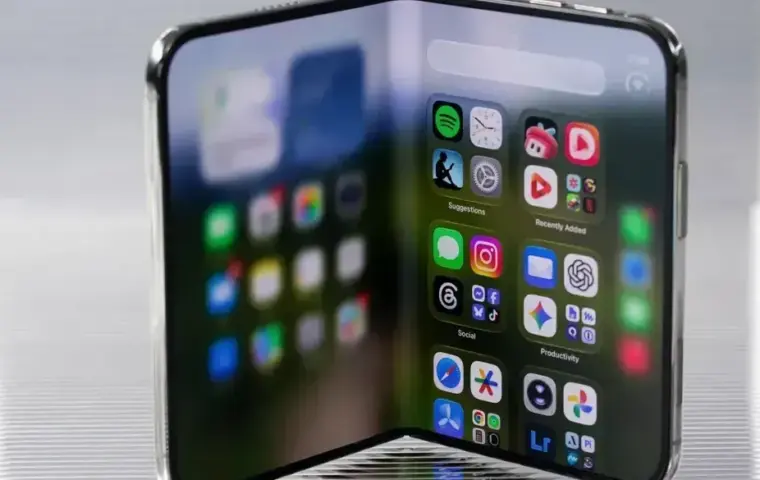
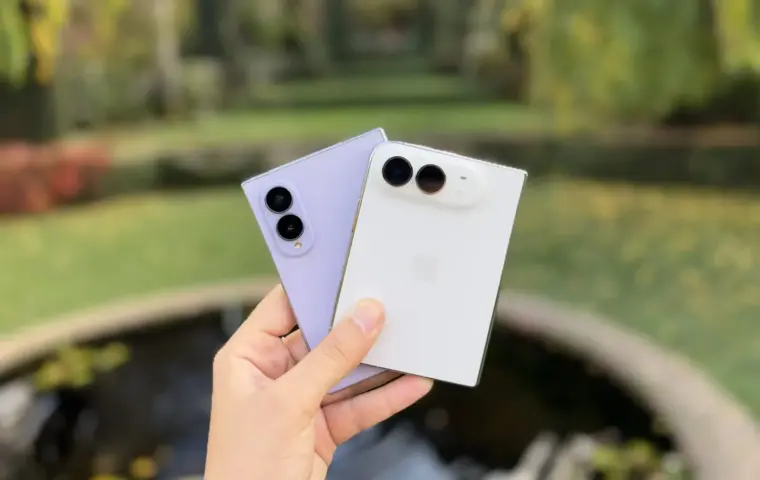
These maintenance patches arrive amidst a flurry of hardware excitement for the brand, following the launch of the iPhone Duo and updated MacBook models featuring M6 chips and touchscreen ProLED XDR displays. However, while new gadgets often steal the spotlight, these quiet background updates remain essential for keeping personal data secure against evolving digital threats.